[–] 1718627440 2 hours ago
[–] 1718627440 1 hour ago
For point based train control systems, operation of a train is only enforced at every signal (and on the way in approach at specific points), this means e.g. that a train does not run over a red signal, does not drive faster than the maximum speed, and has acknowledged speed limits.
For line based train control systems, that supervising happens continuously over the whole track.
Since the physical signals and sensors are expensive in installation and maintenance and railway capacity depends on the number of blocks on a track, line based train control systems support virtual blocks. This means that the signals and sensors are not physically there, but simulated by computers (on the train and signalbox). From the view of the point based train control that means multiple trains are in a single block, because it does not know about the virtual subblocks. When a train is running that only supports point based train control it can only use whole blocks, so the capacity is simply reduced, but it is still safe, because every physical block is also known in the line based control system.
When the line based train control system stops being in use, the fundamental constraint of the point based train control system is being violated: there are multiple trains that are in a single block, and hence not actually protected by a red signal in between. This means that you must ignore the signals until every train has crossed at least one physical signal.
(This is speculation:) It seems that that the operators assumed that there is still a safety system in place, that they can rely on. Hence they did no tell the trains to use manual operation, (which might also require driving by sight [max. 40km/h], but not necessarily, I don't know the proper procedure in Spain), but told them to fall back to the normal safety system. It's reported that some train drivers and dispatchers questioned that, but that can also be an translation error and instead them repeating what was said, as is proper safety procedure. But the point based train control system will show a green signal, even if there is actually a train in front, because it is in the same block as you, but the signal shows whether you are allowed to drive in the next block, not into the current, as you are already in the current block. This seemed to be what happened here, the second train saw the green signal thought they are back in the automatic safety system and accelerated to 200km/h, not knowing that there is still a train in front. The first train should have also started driving, but did not, due to an error in the train. In normal situations this should never cause an accident, but in this case the accident would not have occurred if that wouldn't have taken place, but that would have been simply by luck.
You can see the green signal in some of the pictures, which to me looks really weird, because I would expect to put all signals to red in the case of an accident. I would expect to do that, while you are calling the emergency number, but I do not know if that is the procedure in Spain. You also see in the pictures that the whole cluster traveled about a train length and that the last carriages of the first and the first of the second train are merged into one. This indicates a surprisingly high speed for the crash, above 100km/h. That fits the explanation of the second train not being able to see the first until directly up to a few 100 meters before.
There were actually more trains in that block, so it's pure luck, that there were "only" two trains involved in this accident. Also some claimed, that there was a curve directly before, so the second train couldn't see the first until directly up to the accident. This would not have prevented the accident, it would have just reduced the involved crash speed and hence reduced the number of dead people.
It's quite ironic, that the accident would have likely not happened in case of no safety system being present.
---
Actual classical collisions of two trains like in this case are quite rare, because that's like the first purpose of every train control system, which exist since the 1870s. The accident from January this year in Spain was also a collision, but because a train derailed, while another train passed it. This can't really be prevented by a current train control system, other then not allowing the derailment to happen in the first place. Derailment in carriages is actually not rare at all, but daily, it's like going slightly on the shoulders of the street with your car, but train derailments are.
The accident from Meerbusch-Osterath from 2017 is similar in that is was also a collision. The cause itself is not really similar. The normal train control also failed, so the trains need to be operated manually. For that it was still relied on the automatic train detection and labeling system, but that had a bug (and some operator error due to a bug, this is simplified) and showed the number of the second train, where the block of the first train was. So they allowed the second train to advance. They did have contact with the first train, because they noticed something was wrong, but that driver didn't properly speak German and also failed to look out of the window directly where a hectometer sign was, so he couldn't tell the dispatchers were he actually was. The dispatcher forgot to tell the driver of the second train to use drive by sight (40km/h), so he accelerated to full speed (120km/h). The accident only caused 40 injured people and no deaths, because the second driver saw the first train. The accident happened at night, in the dark and at a speed of 85km/h. Train dispatchers are supposed to keep track of the trains and the actions they do too, but since the automatic train detection and labeling works most of the time, it becomes easy to rely on it.
The accident from Fallersleben from 2002 is similar, because the original failure of LZB and fallback to PZB is the same. Hence there was also more than one train in one block. The signalbox software told the second train to advance to full speed and the first to stop. This would have caused a crash, but the train driver of the second train noticed, that couldn't be and notified the dispatcher who then told them to not proceed, hence the accident didn't happen. This caused it to become mandatory to let the first train to drive again operate on sight [40 km/h].
[–] swiftcoder 16 hours ago
[–] dimal 8 hours ago
Here is a plausible alternative explanation:
They’ve probably seen false warnings over and over and overridden them enough times that they lost sense of the risk. They need to keep trains on schedule, using a buggy system, with a manager looking over their shoulder. They override the warnings over and over, nothing goes wrong, and they forget that it may actually be right. Look at the Challenger explosion, Chernobyl, or any other failure like this, and there’s usually a bureaucratic process that has run amok, and the individual is just following perverse incentives that have been socially normalized over time.
So I’ll wait until I have more information before I proclaim this as human negligence and the system doing exactly what it’s supposed to do. We don’t know how often it was doing the wrong thing and confusing the fuck out of the human.
[–] peri-cl 8 hours ago
Normalization of deviance,
https://hn.algolia.com/?query=normalization%20deviance&type=...
[–] whycome 6 hours ago
[–] gregglain 3 hours ago
[–] swiftcoder 7 hours ago
Negligence is not limited to the single human who issued the order. it's pretty unlikely that their order could have caused this without a significant amount of other negligence that eroded the safeguards. Nevertheless, the negligence is human, not machine in nature.
[–] toss1 5 hours ago
[–] crote 16 hours ago
This isn't a game of Hot Potato where the last person touching it goes to jail for gross negligence. You have to look at it through a Swiss Cheese model: every individual safety layer can and will have holes, but a disaster can only occur when all of those holes align.
Why did the LZB system fail? Why did the train dispatcher use the wrong backup procedure? Why did a backup procedure with zero safety checks even exist? Why did the train operator accept this backup procedure? Why did the train allow high-speed driving under those unsafe conditions?
It does indeed seem like the train dispatcher made a big mistake, but that was far from the only thing that went wrong, and it would be myopic to use him as the scapegoat for a far larger systemic issue.
[–] Zigurd 7 hours ago
[–] sznio 8 hours ago
[–] bobthepanda 6 hours ago
[–] avereveard 16 hours ago
[–] barbazoo 10 hours ago
[–] gregoriol 9 hours ago
[–] larodi 8 hours ago
[–] kazinator 9 hours ago
Someone was driving the train who couldn't estimate the stopping distance relative to speed.
If a car is stalled in the middle of the road, and you hit it, that's on you. 200% if a reflective warning triangle was up 100 meters back.
[–] bobthepanda 9 hours ago
At least one of the failures here is that the dispatcher authorized such a high speed, in other systems I am familiar with, generally the procedure with a signal fault is to crawl at a speed such that the train can stop in line of sight distances.
In fact, that is the Spanish protocol, which for some reason was bypassed by dispatch even after the train driver had questioned it:
> Under normal protocols, the driver would be expected to continue moving at a maximum of 40km/h according to their line of sight, and not at normal speed on a track designed for speeds of up to 200km/h.
[–] stetrain 9 hours ago
Air travel is as safe as it is because we don't stop the investigation at "pilot error" but instead ask why the pilot made the mistake, and why a single mistake was able to lead to loss of life.
[–] mdemare 5 hours ago
Rough estimate: by car, you can travel from Lisbon to Talinn (4000km) 100,000 times before expecting to die; by train, almost 4 million times, by plane 400 million times.
[–] pixl97 9 hours ago
You are 100% dependent on your safety and monitoring systems because almost every problem that could come up is beyond the horizon of your human senses. Stopping distances are in thousands of feet to miles depending on the train size and weight. Add any curves and that's far beyond your visibility.
Then you add in management complaining that you're too slow and you need to do things faster and cheaper or you'll lose your job. Things turn from solution culture to blame culture.
Then you add in false errors and warnings in a system that teach you to ignore them and an upper management that doesn't fix them.
Then you have the day like hundreds of others where warnings are going off, management is yelling, but this time there is a stopped train around the corner and everyone dies.
This is a systemic problem.
[–] SkiFire13 7 hours ago
The stopping distance for a train this size and this fast is around 2km. Good luck estimating that by sight. There is a reason the normal protocol has a 40km/h max speed for traveling according to line of sight, which the driver was told wasn't needed.
[–] ahelwer 9 hours ago
https://komonews.com/news/local/13-year-old-boy-killed-while...
[–] skissane 2 hours ago
Here in Australia, a member of my family was involved in a fatal accident with a pedestrian, around 20 years ago. They put him on trial even though the case was weak, and then the prosecutor moved for dismissal part way through the trial. But, what people told us, is prosecutors are encouraged to take weak cases to trial because dropping the case part way through the trial is more politically palatable than refusing to bring it to court to begin with.
[–] maest 54 minutes ago
[–] wat10000 8 hours ago
On a surely unrelated note, car travel is by a substantial margin the most dangerous mode of transport most of us ever use, and the most dangerous activity most of us routinely engage in.
[–] wjnc 16 hours ago
[–] jonny_eh 9 hours ago
[–] Maken 15 hours ago
[–] 1718627440 15 hours ago
[–] djankauskas 7 hours ago
[–] swiftcoder 13 hours ago
[–] 1718627440 12 hours ago
[–] iSnow 5 hours ago
[–] 1718627440 5 hours ago
[–] siva7 7 hours ago
[–] 1718627440 16 hours ago
[–] swiftcoder 15 hours ago
Throwing up our hands about how hard a problem this is seems like a ridiculous position to stake. If we can design self-driving cars, that operate safely in far less controlled environments, we can figure out the linear offset of a large vehicle traveling along a physical rail running along a fixed pre-determined path.
[–] iggldiggl 5 hours ago
Self-driving cars aren't supposed to drive quicker than they can look ahead, which makes the problem way easier because you don't have to figure out how to detect obstacles ahead of time and can simply rely on vehicle-local information to stop if necessary. And because cars can brake way more rapidly than trains, it means you can still drive reasonably quickly even within that limitation.
Plus in an emergency, cars have steering as an additional degree of freedom to attempt getting out of any nasty situation that may have developed.
(And of course the socially expected safety standards for cars are quite a bit lower than for public transport…)
Trains on the other hand have braking distances on the order of a kilometre or so, and high-speed trains at full speed several kilometres, so trying to get by on local data only is hopeless and the usual strategy is instead having central signalling system that can accurately track trains and coordinate their movements.
[–] 1718627440 15 hours ago
> If we can design self-driving cars
We can not design self-driving cars to the safety standard that is required for railways. They are way less safe than the current half-manual system for railways. What you suggest is using less automatic safety systems than what we currently do.
[–] knottn 14 hours ago
[–] Fargren 9 hours ago
I don't think that's relevant to trains. Cars can avoid a collision much more easily than trains can. Cars can swerve, and if they are at a distance at which line of sight tells them they will hit an obstacle, they are moving slow enough to stop before hitting that obstacle. Trains have to stay on tracks, and they need up to 4 kilometers to stop moving.
The constraints are very different, so the solutions and tradeoffs will be different too.
[–] 1718627440 14 hours ago
Current operation of a train is basically self-driving and supervising driver. So if you suggest "just use self-driving", you make the system less safe, not more, because it means just getting rid of the human supervisor. This is not currently done, because it would be too insecure. It might be done in the future, but rather because less safety is going to be accepted in favor for getting rid of the costly human.
A self-driving train will happily cause a crash, if the target is "drive with high-speed in that segment currently occupied by another train". The issue is that that becomes a target, not that there is a human in the loop.
[–] wewtyflakes 7 hours ago
[–] 1718627440 6 hours ago
But there was a recent incident in Germany as well (https://en.wikipedia.org/wiki/Burgrain_train_derailment), which is somewhat similar to the earlier accident in Spain this year. Targeting high value projects, while not paying for proper maintenance is not something that only happens in a single country.
[–] eldaisfish 7 hours ago
[–] IAmBroom 8 hours ago
That is completely false. PTC does that, and we've had it for several decades. There are several self-driving cars operating in the world right now. I have never heard of a PTC system causing accidents; those occur in places where the system isn't required (like entering Grand Central).
You keep pretending that avoiding train collisions is too magical to achieve with current tech, but train traffic is easy to limit (but slightly harder to optimize), and systems exist to do that, because rail is unique amongst all forms of travel: if you drop speed to zero for any trains at risk of collision, they are safe. Planes will plummet; most cars are human-operated and you can get rear-ended, etc.
[–] 1718627440 6 hours ago
And they somehow work with radar, lidar and GPS from inside the train? No they work with classical block based systems and on signalboxes. So all the safety systems are outside of a train.
> You keep pretending that avoiding train collisions is too magical to achieve with current tech
Huh?? Railway interlocking exists for more than a century. It's very safe and I didn't wrote anything contradicting that.
[–] Pragmata 16 hours ago
If I can have reasonably accurate gps readings of my phone while I'm on the train, there is zero reason for train companies to not have systems that are at least as accurate.
[–] lxgr 4 hours ago
Aviation also doesn't exclusively rely on GNSS positioning, so why should train protection, given that it's also extremely safety critical?
[–] cyberax 2 hours ago
My car's GPS does, using dead reckoning.
Trains can also use dead reckoning.
/me checks notes, I've heard that they move on inflexible things called "rails" that almost never change the location.
[–] 1718627440 37 minutes ago
Also the hard part is knowing the position of the others and their trajectory, which changes in between moving towards them and is done by a third party. The normal passing distance is smaller than the width of your vehicle and you can only change your own direction every few kilometers. That means that the others trajectory towards you can only become known after you are already past your last opportunity to change your trajectory and even within your breaking distance. Good luck!
[1] Friction for cars on the road is 0.010-0.015, for trains 0.001-0.002; train speed 120 km/h * 7.5 = 900 km/h equivalent for car; that's not even a high-speed train.
[–] AnimalMuppet 10 hours ago
"Reasonably accurate GPS" trying to determine which track you're on at 150 mph is not as simple as you make it sound. Yeah, it can determine how far along the track you are. But when you get two trains moving toward each other, each at 150 MPH, do you really trust that GPS to tell you that they're on different tracks?
[–] busywaiting 9 hours ago
Keeping track of which parallel track a train was on automatically was a solved problem a hundred years ago, using relays and lights and hard-wired logic. Adding computers and GPS greatly increases the precision with which dispatch knows position and speed along the track, but knowing which track has not changed in the last century.
[–] iggldiggl 5 hours ago
What we're talking about here is some sort of TCAS-equivalent for the case where the central signalling is down – while it's easy to accurately localise trains with the aid of a central signalling system that authoritatively knows about the infrastructure layout, it's quite more difficult when you're trying to do the same thing in a decentralised, train-local fashion.
[–] pixl97 8 hours ago
Oh, they can, but it's usually a very traumatic event.
[–] esafak 10 hours ago
[–] brookst 9 hours ago
It's not impossible. But handwaving GPS placement of trains at the correct location, direction, and track deserves more than a handwave as trivial.
[–] AnimalMuppet 10 hours ago
When Google Maps gets wrong what lane I'm in, nobody dies. It can be right 99% of the time, that's good enough. It's not good enough for a train system, though - at least, I suspect it's not. I'd want a lot more than "it works in my car" before I trusted it.
[–] lxgr 4 hours ago
As a passenger, I'm very glad software engineers haven't (fully) taken over aviation and railway safety yet.
[–] kube-system 9 hours ago
[–] giovannibajo1 16 hours ago
[–] IAmBroom 8 hours ago
Forests are irrelevant; rail right-of-way contains no trees, and is wide enough to assure clear "view" of satellites.
[–] 1718627440 6 hours ago
[–] lxgr 4 hours ago
Absolute nonsense. Do you have any idea how long some tunnels are?
[–] 1718627440 16 hours ago
No, what I describe has nothing to do with the companies, that's the research state. It's just an indictment of you making bold statement about a subject, you don't now enough about.
> I can have reasonably accurate gps readings of my phone
Would you dare to cross on a rope over a deep valley, blind using only GPS readings of your phone? Because that's kind what you are suggesting, expect you also move a few hundred other people.
[–] swiftcoder 16 hours ago
Hang on, this is nothing at all like that - trains run on fixed tracks. The only bit of data we are interested in for collision avoidance is the linear offset along the track. Even the shittiest GPS fix of all-time would give a good-enough intersection with a fixed path to avoid crashing into a second stationary train in the open country-side (do you see any satellite line-of-sight blockers in the crash footage?)
[–] 1718627440 15 hours ago
So that is naive, but assuming that would be all that you need, with GPS you would also need the positions of all other trains. But why would you transmit all this information to every train, instead of just computing the collisions in a central node? (That's what is done now.) A better fit for what you suggest would be radar, and this does exist. [1] But that's where your original assumption is naive. You regularly pass other trains within <2m at high speeds, so linear offset is not all you need.
[1] https://www.dlr.de/en/kn/research-transfer/projects/next-generation-train/rcas-railway-collision-avoidance-system[–] collabs 15 hours ago
There are optimizations possible like make segments smaller etc but the original algorithm is trivial. If we can't figure things out, we make segments longer and we slow down the trains until we can. I am positive for a sufficiently large track segment and a sufficiently slow train, we can always answer the question with a no.
[–] jdmichal 9 hours ago
[–] 1718627440 15 hours ago
[–] Pragmata 10 hours ago
[–] 1718627440 10 hours ago
[–] djankauskas 7 hours ago
[–] 1718627440 6 hours ago
[–] lxgr 4 hours ago
There are also other solutions, e.g. LZB uses a phase change of the signal every 100 meters as an additional precision signal.
[–] 1718627440 3 hours ago
[–] djankauskas 6 hours ago
[–] 1718627440 5 hours ago
[–] lxgr 4 hours ago
Isn't the ability to do so the basis of operation for e.g. the German LZB train protection system, which has been around since the 1960s?
If you mean that train protection systems don't (exclusively) rely on self-reported positions, your statement makes a bit more sense, but even that is changing with e.g. newer ETCS levels which do rely on self-positioning more and more.
[–] 1718627440 3 hours ago
I did not say "train systems are ...", I said "trains are ...". This is referring to e.g. that odometry based on wheels results in a drift. GNSS is to imprecise and unreliable. I'm aware that you simply use balises, that's what I meant with "markers in the track". However that's based on the infrastructure again, so it's again not trains on their own.
https://news.ycombinator.com/item?id=50293093
It was simply supposed to be an example how GPS sounds like it should easily solve a problem, but does not without additional measures, that then do not need GPS anymore.
[–] wjnc 14 hours ago
And some problems are just _open_ to outside looks. My assistant tells me that the room for error in trains on one dimension ('left - right') is mere 10s of centimeters. I understand that problem. But what track you are on, isn't that obvious to the human in the cabin? (Again, simplifying, not flaming. Production ready safety is _hard_.) So could a vision based solution help count tracks from left to right? (Assistant: "US PTC, on about 54,000 route-miles, uses GPS for the lead locomotive plus crew-entered track information and switch position".) So you use the dimension that matters most in crashes (forwards / backwards) from satellite, augmented with vision or human based left-right positioning. Some trains already have sensors to sense things like leaves on the track to adjust speeding and braking... So the sensor based approach is already there.
Perhaps I am read as suggesting that the problem is easy, and that is not my intention. But for cars this was solved decades ago for routing and years ago for self-driving. I use that daily. Flying is organised with a very clear 6 sigma approach. Crashes are nearly always situations where events / risks stack. Trains (in Spain)...?
Tl;dr - Safety is a function of (human; process; technology) and there is clearly something lacking for trains, when compared to other types of transport.
[–] 1718627440 13 hours ago
> Would you mind sharing some more of the why it is still an open problem?
Because for train sensors, there is a small drift which accumulates too much, hence it is synchronized by magnetic position markers in the tracks.
> I understand satellite positioning isn't definitive
Yes, and the point is it might be some solution if we would have the safety systems from 1860. But we do not and hence it needs to be more accurate than the current system, and it is not and in addition also more expensive (and subject to remote influence and reliance on potentially adversary nation states).
> Sorry for the bleak introduction of economics
No, economics is basically the primary constraint for safety. We could pay million people to make sure a single person does not stumble if we want total safety, but that's completely pointless, and also these million people would starve, because no one is producing food anymore.
> But even as a tertiary or lower risk mitigating factor
But for that it's too expensive and still unreliable. There is RCAS[1], which I already linked elsewhere in the thread. That's basically cutting edge and too expensive to introduce everywhere. Also previous safety systems are already not rolled out enough, which is causing these accidents, so rolling out yet another expensive system is not going to improve much.
> But what track you are on, isn't that obvious to the human in the cabin?
Yes, but if it is already known, why use GPS to calculate the same information with more error?
> So could a vision based solution help count tracks from left to right?
If the train driver or dispatcher makes use of vision to assess the train position, the error will be higher than the current sensor/electric-resistance based system.
> Assistant: "US PTC [...]
BTW, that seems to be a verbatim quote from https://www.railwayage.com/cs/the-way-forward/
> US PTC
According to Wikipedia, ASFA being introduced in 1975 is rolled out in the entire Spain network. ETCS which is the European standardization seems to be rolled out on all high-speed lines or currently being rolled out.
> So you use the dimension that matters most in crashes (forwards / backwards) from satellite, augmented with vision or human based left-right positioning.
Duh, that just sounds like trains would be operating blindly in space currently and need to assess their approximate position.
> Perhaps I am read as suggesting that the problem is easy, and that is not my intention.
No, the issue is that you are suggesting far more complicated solutions to already solved problems, with simpler systems in operation for decades. The current system is that nobody in the train even has a say on where the train goes, so the problem you are trying to prevent doesn't even exist. This IS why it's way more safer than a car. There are movement authorities, that define from where you are allowed (and have to) drive with your train. The problem is not, that the train driver isn't able to know where he is and hence drives wrong or too far (that would be prevented by the on-board safety system), but that the movement authority itself is faulty.
On an up-to-date signaling box (withing the past 6 decades), even the train dispatcher is no say in safety questions. You could put a monkey in charge of it. There would be chaos, but they would not cause a crash. The current job of a dispatcher in normal operation is to assign resources to prevent deadlocks and to implement vaguely defined priorities. (Basically the equivalent of the public thinking a programmer is a code monkey, while the actual point is clarifying stakeholder interests.)
The actual issue here is, that while these safety system have a very small false positive rate, they do have a too large false negative rate for there to be an acceptable availability. Hence in the latter case, the human needs to take over and then you are back to a much higher false positive rate. The issue would be alleviated by relaxing the constraints on cost per availability. Either by allowing for less availability or by reintroducing more humans, so that the system situation can be assessed by humans directly.
These accidents are caused as follows: the automatic system fails, because the internal state of the system does not match the actual state of the world. Hence the human needs to take over. But the human also needs to rely on some system to know the world state. Which systems can he trust, given that the whole situation is that the systems report that he can't trust them? So he needs to make some decision and in most cases, that decision is still correct. But there is still an error rate to that, and then something like what we are discussing happens.
> But for cars this was solved decades ago for routing and years ago for self-driving.
This is absolutely not solved for the cars, and to the sense that it is, it was solved and rolled out from the 1870s onward for railways using mechanical computing systems, the switch to using electricity happened in the 1910s.
> Flying is organised with a very clear 6 sigma approach.
You are correct, that aircraft safety systems need to be designed to a higher reliability than railways, because on a rail you can always stop in case of an error, while in the air such a choice doesn't lead to a safe state. But if you compare these safety systems, basically aircraft is operated like railways used to be operated in the 1920s. (My peers actually had a task to compare them and find ideas from one that can be applied to the other. While there is a lot of automation to be taken from rail that can be applied to the aerial industry, there is not really much that can be applied the other way.) It is also operated with the amount of personal than 1920s railways. That's because there is a lot of money in aircraft, while railways are mass-transit and need to be cheap. If you would operate today's railway with the amount of human oversight than in the past, it would be a lot safer than aircraft.
> there is clearly something lacking for trains, when compared to other types of transport.
What are you talking about? Railways are so much safer than cars. https://news.ycombinator.com/item?id=50288518 Yes, there are less accidents in planes than in trains, but this is due to what I already explained.
[1] https://www.dlr.de/en/kn/research-transfer/projects/next-generation-train/rcas-railway-collision-avoidance-system[–] wjnc 11 hours ago
[–] IAmBroom 8 hours ago
[–] 1718627440 6 hours ago
That's a research topic, because the infrastructure companies would like to not pay as much for maintenance and still have a high sequence of trains. Also with track based train control systems you can only have very high resolution in specific places, where you place your track-side infrastructure, but it would be nice to have that resolution anywhere you like.
[–] lxgr 3 hours ago
I guess a much less dense and largely overground network, mainly used by fairly slow moving freight trains as opposed to highspeed passenger connections, changes requirements somewhat.
[–] 1718627440 3 hours ago
I mean they are systems that rely on GNSS in Europe, but no safety systems, that would be simply to unreliable. For example I believe the railway announcements in Germany to depend on GNSS. They are also unreliable.
[–] cryptoegorophy 5 hours ago
[–] thatfrenchguy 7 hours ago
[–] tencentshill 9 hours ago
[–] 1718627440 16 hours ago
Also the fallback procedure is also aided by automatic systems and a sizable number of accidents in the past were caused by that information being faulty.
[–] julik 16 hours ago
There will be a so-called "train order" allowing passage of a specific section ignoring the safety system warnings, which has strict validity limits both in time and in the area where it applies, usually denoted by specific hectometric mileposts
When cab signaling is involved (LZB is one of these) and it malfunctions, the entire system normally changes to "driving on sight only" - which indeed limits the train to 40, 30, 20, sometimes - 15 km/h (see https://fr.wikipedia.org/wiki/Marche_%C3%A0_vue) or the line gets switched to lineside signaling - if it is available.
I don't know how you could violate all of those rules - both from the driver's side and from the traffic control side - but it sounds absolutely horrible. Like an override of at least 2 (if not 3) very explicit safety margins.
[–] 1718627440 1 hour ago
[–] dist-epoch 15 hours ago
They were the wrong orders apparently.
[–] AdrianCX 16 hours ago
I remember a long time ago I was stuck in a train in a field a considerable time because of a similar failure and conductor just wouldn't move unless green
I was expecting the same here, conductor is the first to die so just refuse until the idiots fix their system
[–] 1718627440 16 hours ago
What exactly?
A conductor always just gets a movement order. They are not able to assess whether the track is clear, that's the reason why the signalling system exists in the first place. How they get that movement order doesn't necessarily tell what the security steps were to back it.
Of course an attentive conductor can notice and mention there something being weird ("Doesn't the other train normally arrive first?"), but that's a rare lucky occasion, nothing to be relied on. And they just need to swallow the answer ("No, you go first today...") anyway.
> and conductor just wouldn't move unless green
The conductor won't ever move unless they get a movement authority, which most of the time is a green signal.
[–] AdrianCX 16 hours ago
[–] AngryData 48 minutes ago
In some industries that is how they keep costs low while pretending they are being safe. They have alarms or procedures that say something is bad or wrong, but fixing some problems costs more money than it saves so they want them to be ignored, and managers will get angry and admonish you or eventually fire you if you keep following procedure and stopping to check problems. So eventually they build a team of people essentially trained to ignore problems. Which is why many oil pipelines still use ancient and unreliable leak detectors, they know those systems are unreliable and the operators will get alarm fatigue from the 200 false alarms, and that way they also ignore when a real problem happens, and worse case for the company they scapegoat the operator. They don't care that 2,000 gallons of oil leaked into the wilderness and poisoned the land if it would cost 2,000+ gallons of oil profit to shut down and repair the leak. They have a financial interest to not fix it.
[–] 1718627440 16 hours ago
[–] AdrianCX 15 hours ago
Being a snowflake here has 2 benefits:
1. Getting company managing tracks to fix the lights (they need to deal with angry customers and pay off damages for delays and more), so there's a direct path from unreliable lights to economic damage.
2. Avoid crashing and killing yourself and passengers on the offchance the person on the radio is a moron
[–] robhlt 15 hours ago
It cannot be bypassed, if an operator must go through a red they have to manually reset the e-brake on each car once it passes the signal.
[–] _trampeltier 16 hours ago
[–] wafflemaker 16 hours ago
[–] _trampeltier 16 hours ago
[–] masfuerte 7 hours ago
[–] 1718627440 16 hours ago
[–] inglor_cz 7 hours ago
Dyatlovs seem to be born everywhere.
[–] juliushuijnk 8 hours ago
[–] Zigurd 7 hours ago
Your suggestion about limiting speed after a shut down is a good one. On top of that, the rail operators should have spotted a trend of repeated safety system overrides and investigated why that was happening.
[–] 1718627440 1 hour ago
[–] aquafox 8 hours ago
[–] askvictor 2 hours ago
Exactly. Which means a whole bunch of other people allowed for this situation to occur. So it isn't one person responsible for this mistake.
[–] notenchange 16 hours ago
That’s why people here, when they hear the fire alarm they just wait for it to go off: the probability that it is actually a fire is minuscule… but the alarm triggers a lot.
Not sure how to actually solve this… but I’m also not making excuses for what happened. High speed trains is not the same as a fire alarm in some office building, the people in charge should be held responsible somehow.
[–] PaulDavisThe1st 10 hours ago
Because of this, I discovered that (apparently) NY Fire Department charges $5000 per false call on an alarm system directly connected to the dispatch system.
Somethng to think about.
[–] jcrawfordor 7 hours ago
Honestly it's remarkable to me to think that anyone ever gets to that $500 "excessive" tier, I've had one false alarm where the fire department attended in years of having an alarm system and I was mortified. felt like the biggest idiot in the world.
[–] brudgers 7 hours ago
[–] jonah 10 hours ago
[–] Maxion 9 hours ago
[–] js2 8 hours ago
https://www.nfpa.org/news-blogs-and-articles/blogs/2023/03/0...
I wouldn't think code dictated the alarm type. (I just replaced all nine sensors in my home due to age and went with all photoelectric this time and it was less than six months before I had my first false alarm. Never had any false alarms with previous ionizing type.)
[–] femto113 8 hours ago
[–] Animats 7 hours ago
We once got an alarm because the heating element in a computer room air conditioner had turned on for the first time ever. It was defective and started to smoke. Smoke detection tripped, buzzers sounded, lights on a panel showed where the problem was, and alarms went off in the security control center. But this didn't trigger building evacuation or full power down. That took confirmation from a second sensor.
Someone ran into that computer room, saw smoke coming from the A/C unit, and pulled the big red power switch, installed by the safety people, on the air conditioner. Then we had time to shut down normally, the safety people came to clear the alarm, and the HVAC people came to fix the problem. I kept the burnt heating element on my desk for a few days for people to see.
This is typical for big industrial plants. Bad stuff will happen, and you have procedures for it.
[–] askvictor 2 hours ago
[–] childofhedgehog 5 hours ago
[–] JumpCrisscross 5 hours ago
[–] infecto 10 hours ago
[–] futureproofd 9 hours ago
[–] munk-a 8 hours ago
[–] Kinrany 9 hours ago
[–] rtkwe 9 hours ago
[–] ralegh 9 hours ago
[–] mindslight 8 hours ago
[–] bell-cot 8 hours ago
[–] munk-a 8 hours ago
You never want to supply any reason for someone to demur about reporting a fire.
[–] eastbound 7 hours ago
[–] uniq7 9 hours ago
[–] comeonbro 8 hours ago
> Healthcare: The constant sounds of alarms and noises from blood pressure machines, ventilators and heart monitors
> Amber Alerts: sent to cell phones as far away as [...] 15 hour drive
> "known to the state of California to cause cancer"
etc
https://www.youtube.com/user/USCSB
See also a million USCSB industrial disaster postmortems
[–] prmph 5 hours ago
Should probably be: "known to the state of California to be a class N carcinogen"
[–] eastbound 7 hours ago
I prefer to risk my life every day at not knowing what the government thinks is really important for me to know.
[–] 1718627440 16 hours ago
[–] karmakurtisaani 16 hours ago
[–] mercer 14 hours ago
[–] thaumasiotes 7 hours ago
I was interested to find a discussion of the trolley problem in a book of out-of-copyright Norwegian-region folk tales (in English translation) that Amazon recommended.
[–] jryle70 5 hours ago
[–] coopykins 16 hours ago
Guess whats the consequence of that? Less and less people pay attention to the alerts.
[–] ricardobayes 16 hours ago
[–] cbovis 7 hours ago
Government officials are terrified of taking the blame for another Valencia style flooding catastrophe so any hint of rain blasts the mobile phone emergency system. Once the alert has been sent the officials can feel safe in the knowledge that they've done something.
[–] jonny_eh 9 hours ago
[–] jameshart 9 hours ago
[–] 1718627440 3 hours ago
[–] jonny_eh 6 hours ago
[–] throwitaway222 7 hours ago
[–] sznio 8 hours ago
fix the alarms? I only had one false fire alarm in my life. and thankfully zero real ones. it's possible.
do fire drills? if alarms get ignored, and you can't reduce the false-positive rate, then introduce fake alarms and monitor the response?
[–] whycome 8 hours ago
(...on track)
[–] eastbound 7 hours ago
[–] 1718627440 3 hours ago
[–] pelagicAustral 16 hours ago
This literally happened to me last night, I was having dinner at my apartment, and suddenly I start hearing a smoke alarm, but not quite inside the apartment, I just kept having dinner thinking "bah, someone probably burned a toast".
Then it wont stop, I walk to door and hear people talking, still don't bother enough, wait a few minutes, then go out and my neighbor said "there are three fire trucks down there, I think it's a real one" hahhaha
The hallway was kind of hazy and smelled like burnt food, for sure... so I just grabbed my laptop and went out hahaa.
[–] D-Coder 7 hours ago
The building fire alarm is soooo loud and obnoxious, you _want_ to leave the building at speed. (Which I think is the right way to do it.)
[–] avereveard 16 hours ago
Safety culture is blameless, but only if everyone plays along.
[–] inglor_cz 7 hours ago
I know that this was likely a typo, but it is also a genuinely great word for the sort of attitude related to these situations.
[–] tintor 10 hours ago
[–] kazinator 9 hours ago
[–] gambiting 5 hours ago
[–] IAmBroom 8 hours ago
What I'm saying is: false positives should not be ignorable, and modern systems take that choice away (at least, just before the situation becomes unavoidable in worst-case analyses).
That being said, previous fatal accidents in Spain's high-speed rail have resulted in "primitive" uncontrolled areas between controlled areas. Those SHOULD NOT exist. You are essentially saying "lives don't matter that much here " ($/life).
[0] I work in rail safety.
[–] esafak 10 hours ago
[–] electroweak 8 hours ago
But train traffic systems seem to be a hodgepodge of different systems, perhaps locally grown and driven by the local vagaries of politics and rulemaking.
What a surprising inversion of expectations regarding safety.
[–] djankauskas 7 hours ago
[–] Zigurd 7 hours ago
[–] thr0waway001 7 hours ago
[–] hilbert42 3 hours ago
An automatic failsafe mechanism should be installed to stop/cut the power to the moving train in situations like this, it should work irrespective of any instructions or actions by the controller or the driver.
When safety parameters deemed the Renefe train to be travelling too fast and too close to the Iryo one it should have stopped automatically. Such safety measures aren't rocket science but straightforward engineering, (interlocks, etc.). Over the years there have been too many accidents in situations such as this for such equipment not to be installed.
For a moment I visualized myself in that busy control room and easily making that mistake even though I'd made the correct decision hundreds of times previously. Not only are 69 lost lives a terrible tragedy but the life of the person who made this momentary slip has been ruined forever.
It should not have been allowed to happen. It's worth remembering that Westinghouse brake systems (which are well over a century old) automatically default to on (stop) when there's a fault, and the high speed (now decades old) Shinkansen has very sophisticated stopping mechanisms and has never had a major crash. The question is why such safety measures weren't installed here.
[–] 1718627440 3 hours ago
There are situations where the dispatcher needs to instruct the driver to ignore the road signals and hence also ignore the automatic enforcement of the signals. It shouldn't happen to often, but the real world is always more messy.
[–] bombcar 3 hours ago
https://en.wikipedia.org/wiki/Automatic_train_stop
Any failsafe that can be bypassed manually is just a deferral to humans and eventually will result in disaster.
[–] dang 10 hours ago
What we know so far about Spain train crash - https://news.ycombinator.com/item?id=50286197 - Oct 2026 (84 comments)
[–] fhub 2 hours ago
[–] anonymous2024 8 hours ago
[–] amiga386 8 hours ago
The LZB system, which broke down, had the data you describe. It knows when trains pass over fixed sensors so it computes where they are, and sends data packets to specific trains informing them their current speed limit, and the next, and how far away that is. If the driver won't slow down, the train will.
When LZB broke down, they had to switch to their other system, BSL (fixed block signalling: https://en.wikipedia.org/wiki/Automatic_block_signaling). You can then know the distance to the next block, and if it's occupied or not, but not where the train is inside the block. You can only guess.
In the next few days we'll likely find out if the control centre also fucked up the block signals...
[–] bgnn 7 hours ago
[–] 1718627440 1 hour ago
[–] bell-cot 8 hours ago
[–] maxglute 8 hours ago
[–] ironman1478 5 hours ago
[–] germandiago 7 hours ago
15 or 20 years ago when I took the train it worked well.
Now there are more trains and they increased the traffic like by 70% if I am not wrong and the budget for railway infrastructure by only 17% and it seems to not scale well enough, for whatever reason I do not know all the details.
There are a lot of railway tracks that are not in good state so speed must be lowered. There are incideents and delays routinely, all the time.
This did not happen until like 10 years ago and it has gotten worse and worse since then, not only in high speed trains.
The roads is a mess also: 52% of infrastructure for roads has bad or very bad defects in it.
The thing is that we have a record in government incomings and the services, ALL of them (healthcare, roads, infrastructure...) slowly collapsing.Part of the money is not going to the right places. I think that nearly 40% of the budget goes for retired people. We have 9.5 million pensionists in Spain.
We have to change that system and rationalize government spending and welfare or eventually everything will collapse.
[–] Grombobulous 7 hours ago
Roughly 31% of Japan’s budget goes to social security. They don’t have problems keeping their high speed trains safe.
Cutting pensions won’t make trains safe.
I will also point out that on its own without further context, a high percentage of government spending going toward something doesn’t make that spending irresponsible or misappropriated. In the United States, a very high percentage of federal taxes are spent on Medicare and Social Security. But it should come as no sirprise that a very large percentage of federal income tax revenue is directly appropriated to pay for those things.
[–] Al-Khwarizmi 6 hours ago
https://elequidistante.github.io/graficos-jongonzlz/pensione...
https://elequidistante.github.io/graficos-jongonzlz/pensione...
https://elequidistante.github.io/graficos-jongonzlz/pensione...
And maybe this is the most illustrative:
https://i.redd.it/uwvgxycxhjeg1.jpeg

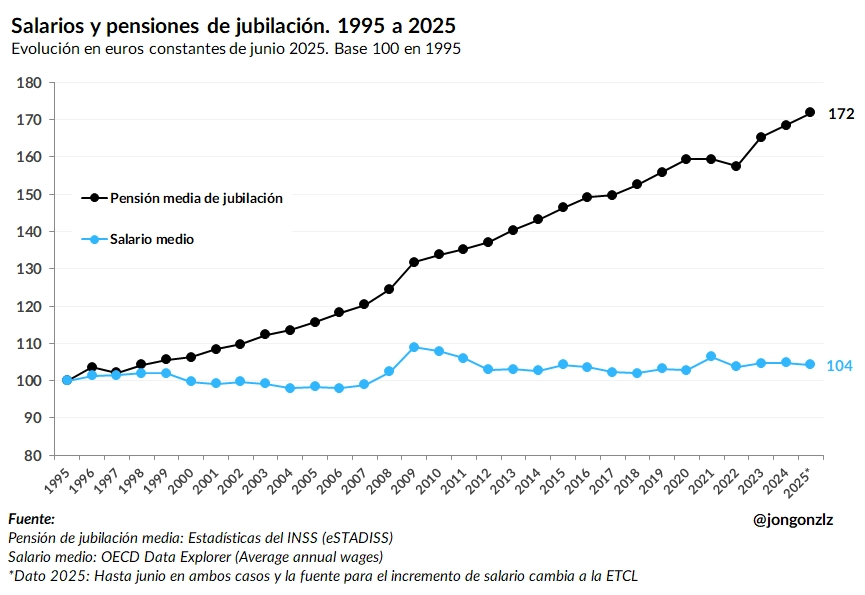
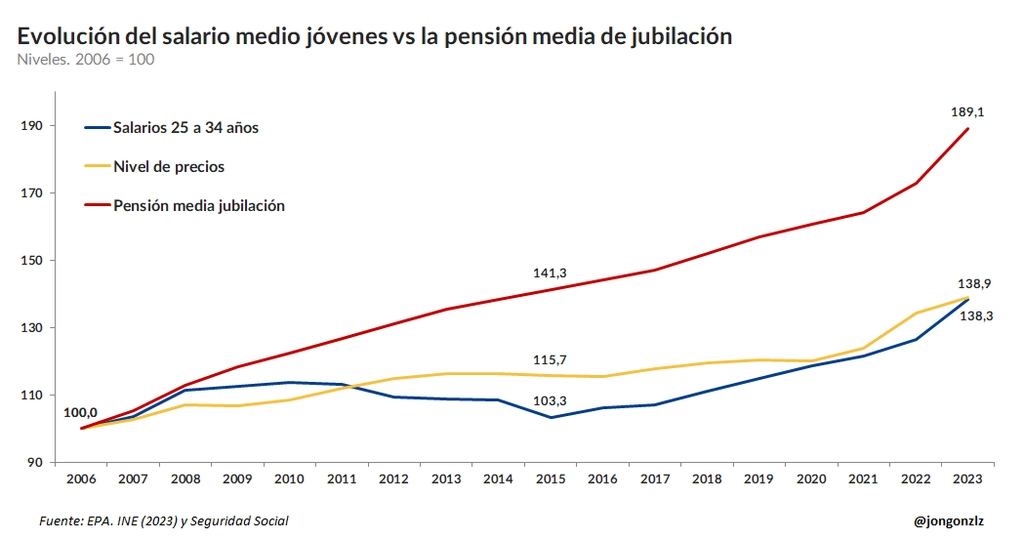
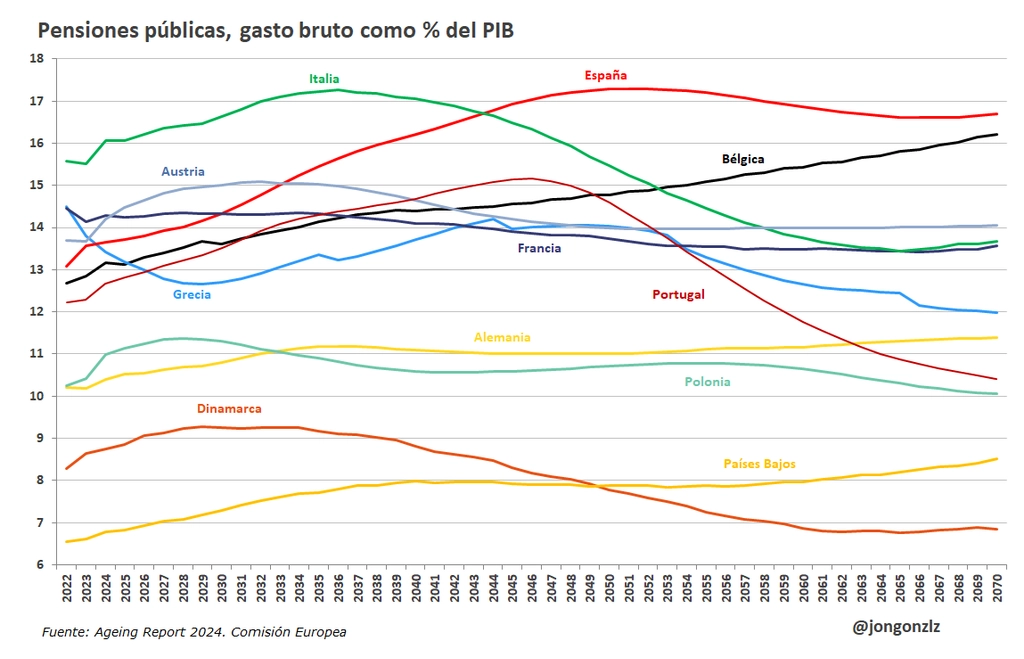
So yes, the reason why we are underinvesting in pretty much everything is basically pensions. GDP is up, tax collection is up, debt to GDP is sligthly decreasing... but pension expenses keep growing at a fast pace so there's less and less money for everything else. And I say this with both of my parents earning the maximum pension, so I don't have an axe to grind, but it's just reality.
[–] bombcar 3 hours ago
[–] germandiago 6 hours ago
I am giving an objective explanation in all honesty: Spain needs a pensions reform probably at some point bc it is 40% of the expenses in the yearly budget, with a deficit and a demographic deficit. This will explode.
If it can be taken from elsewhere, better.
But you know how much are pensions in Spain and know our pension system in detail (it is literally a Poncy system...)? They are often higher than people working!
Whether we like it or not, we need to reform or collapse in the future. I wish it could be taken from elsewhere, but 40% is a lot...
There is a lot of useless expenses in public work in our "federal system" (comunidades autónomas).
[–] Grombobulous 1 hour ago
I agree that good reforms that involve realistic budgets and high levels of accountability are very good things. However, I encourage a lot of caution and skepticism around ideologies that inevitably lead to cuts to benefits.
The USA's pension system replaces a lower percentage of the average wage than Spain's system, and its universal healthcare for pensioners has higher exposure to out of pocket costs. Despite this, the debt to GDP ratio in the USA is higher than Spain, and there is a grand total of one government-operated high speed rail line which is barely high speed despite being 5x more populous.
That's why I encourage caution: cutting pensions won't necessarily lead you to better outcomes, it might just leave you to cut pensions with no improvement in other areas.
I know you are not suggesting cutting pensions directly but what I'm saying is that these types of comments contribute to people "voting against their own interests" so to speak.
[–] LtdJorge 6 hours ago
[–] pofferfish 6 hours ago
[–] square_usual 6 hours ago
[–] Grombobulous 6 hours ago
[–] qurren 6 hours ago
Their trains are safe, but they also have 2X the national suicide rate as Spain, which amounts to about 17000 more deaths per year. I'd attribute a big chunk of that to their work culture treating people like machines, whereas Spain's work culture tends to lean towards treating people like humans.
That isn't an excuse for railway mishaps, of course, but I'm just trying to de-romanticize Japan as some kind of magical perfect place. It's not. They might have gotten their railways right, but they have massive safety issues around mental health.
[–] nbajka 5 hours ago
You clearly have not worked for the average Spanish employer.
[–] naranjito 2 hours ago
[–] xorcist 5 hours ago
But under-maintenance causes trains to stand still and be late. It does not cause them to crash.
Crashes are caused by running at speeds higher than the (under-maintained) rail can support, or (against all rules and every regulation) no cap on speed when the signalling system is down.
The latter can not be solved with more money and resources. It is a culture problem. Rules can not routinely be disregarded for arbitrary reasons, especially not when they are completely in line with common sense.
[–] naranjito 3 hours ago
The Iryo train was stopped and unable to restart, because it's safety system did not allow that until the signalling issue was corrected. The AVE was commanded to move again like normal (200 Km/h or more). When the Iryo reported to be stuck, all the trains in the line should have been notified to stop once more, or go at line-of-sight speeds (40 Km/h). Both options are bad for delays. Current news is that five minutes after the Iryo call, the AVE rammed its back at 160-200 Km/h.
CEO of Iryo company complained 3 weeks ago about LZB being problematic, their trains taking a long time to recover connection. Safe but old, he said. It should have been replaced by ERTMS by 2024-2026.
[–] rwyinuse 6 hours ago
Still I agree, pension systems in most EU countries are unsustainable.
[–] JaumeGreen 6 hours ago
Pensions is 13%PIB which is on the European median.
The problem is demographic. Also take into account that retired people have paid for their retirement.
Your rhetoric is not what I'd like to be promoted as the first answer entering. Just reading the title of the news I knew what kind of messages I'd see promoted.
[–] nbajka 5 hours ago
No, they have not. It's a pyramid scheme. Whatever they put into the system when they worked probably doesn't even cover 5 years of retirement.
[–] jltsiren 2 hours ago
If you choose that (or if your legal system determines that), you need to be proactive with keeping the pension system in balance. While you can change what you promise in exchange for future contributions, substantial changes to what you have already promised can easily require constitutional amendments.
[–] nbajka 5 hours ago
[–] iSnow 5 hours ago
Wait, I thought Spain's high-speed rail network was all ETCS L1 or even L2?
[–] mdurana 4 hours ago
[–] fortran77 2 hours ago
[–] dogscatstrees 8 hours ago
[–] iSnow 5 hours ago
That's where the EU came in and developed ETCS (https://en.wikipedia.org/wiki/European_Train_Control_System) as a modern alternative. Unfortunately, the EU doesn't have the legislative power to force member states to adopt it and also not the money to bribe them. So ETCS is still competing with the legacy systems.
However, the reason for that crash apparently was the dispatcher who greenlit the cab driver to go full speed ahead after the train control system on that track had crashed even though they knew that another train was reporting that it was unable to restart and get going. Procedures in case of a train control outage are clear: all trains can only move at a max speed of 40Km/h - slow enough to drive and brake on sight.
Instead, that train crashed into the stationary one coming from 200Km/h
[–] naranjito 2 hours ago
[–] dogscatstrees 4 hours ago
Apologies in advance for what may be a pedantic and possibly dumb question, but is there a failsafe or guardrail against such forced errors?
[–] djankauskas 7 hours ago
[–] satellites 8 hours ago
[–] steelframe 9 hours ago
I set my favorite agent on the task (Opus 5.5 in the Kagi Assistant), and given the two rail crashes in Spain this year, these are the stats it came up with for "chances of dying" via various modes of transportation between Seville and Madrid:
* EU high-speed rail, long-run average: ~1 in 36 million
* This rail line, counting both 2026 crashes: ~1 in 400,000 to 1.2 million (prior to the most recent crash it was 1–3 million; now ~2.5× higher)
* Flying with a European airline: ~1 in 80 million
* Driving: ~1 in 1 million or worse
Of course this is hindsight. Heightened awareness of risks, higher propensity to overreact to anomalies or alarms, procedural changes, and so forth in the wake of this second crash might push high-speed rail in Spain to be higher than the European average in the future.
[–] loloquwowndueo 9 hours ago
[–] absoluteunit1 9 hours ago
[–] rimeice 5 hours ago
[–] Yokolos 16 hours ago
[–] 1718627440 15 hours ago
I would actually sit in front now. Sometimes you would be able to still get vital information and being actually able to act. But the safe decision would be no to enter the train.
[–] flohofwoe 8 hours ago
You might just as well never leave your bed, that's even safer ;) Train travel is much safer than travelling on roads, and in the same ballpark as commercial flight.
[–] barbazoo 10 hours ago
Optimistically assuming you have a minute to react (I'm imagining closer to 10s), what could one possibly do?
[–] 1718627440 9 hours ago
[–] comrade1234 16 hours ago
[–] enriquto 8 hours ago
Meanwhile no high speed rail between València and Barcelona, because that would somehow erode the power of the central elites.
[–] ktallett 17 hours ago
[–] bigDinosaur 17 hours ago
Sadly we'll probably watch a lot of individuals being blamed/scapegoated for systemic issues, but hopefully even Spanish politics can organise a proper investigation after this many deaths in a single year.
[–] spaniard89277 4 hours ago
Also systems in place not trusted by the workers, which means they're used to bypass them.
It's a systemic failure.
[–] jplrssn 17 hours ago
I don't see how this would fall on the drivers at all.
[–] gpvos 17 hours ago
[–] 1718627440 15 hours ago
[–] pixl97 8 hours ago
A person saying you have a green light when you have a red light is not the same information at all. The probability that something has gone wrong and will lead to disaster is many many times higher.
[–] 1718627440 6 hours ago
[–] crote 16 hours ago
As we also know from the aviation industry, controllers are human and therefore will make mistakes. A controller shouldn't issue a wrong order, but a driver also shouldn't accept an order they aren't certain about, and there should be technical systems backing both sides of that up.
It doesn't "fall" on the driver, but it doesn't "fall" solely on the controller either. It's a systemic issue, and many pieces have to fail for a disaster to happen.
[–] 1718627440 15 hours ago
The aviation industry operates like the railway industry ~1920 (somewhat by necessity).
> You wouldn't drive your car into a lake just because your satnav tells you to, would you?
You are assuming a train driver is equivalent to a car driver. He's not, the analog would be more a repairmen that you always take with you on journeys.
[–] gus_massa 9 hours ago
Also stopping distance for trains is huge. This video for high speed trains says 5km (3mi) https://www.facebook.com/Renfe/videos/%EF%B8%8Fcu%C3%A1l-es-... That is probably at full speed, but IIUC the accident was at half speed so the distance should be like 1.2km (0.8mi).
[–] 1718627440 16 hours ago
A train driver has zero insight in what is going on and where other trains are. They do need to trust the orders they get, if you want to question every order you will never start to drive.
[–] AdrianCX 16 hours ago
That's why it's a union job
Also he's the first person to die on accident so it's that and the safety of everyone else
They do not 'need' to follow others, they just need to refuse unless all safe and green.
If they never start to drive it's the companies problem to deal with angry non-dead customers
[–] stevage 15 hours ago
Every train network has situations where drivers are authorised to proceed against a red signal. Not usually at full speed though.
[–] AdrianCX 15 hours ago
At most face unlikely discipline.
Here they would even have valid reason to refuse - order was given for full speed, regulation says low speed ready to stop.
So a "No, i'm not doing that, you're moron" would be justified.
[–] 1718627440 15 hours ago
[–] kube-system 9 hours ago
[–] knottn 14 hours ago
[–] pixl97 8 hours ago
Then what the fuck is this country even doing with trains.
No, no no, no no no.
Interlock safety systems exist for a reason. In any safety system where the interlock is down you do not resume standard operations. Ever. Why, because there is a book with blood that is 10,000 pages deep that describe the horrific accidents that happens when you do. Might as well be an axiom at this point.
>because somewhere on the track he doesn't see, the asphalt might be broken.
Again, stay away from analogies and safety critical systems.
The person behind the break and speed control of the train is no different from the captain of the airplane or the captain of a ship. They have full authority control to stop the train and refuse to move it until they are sure of the safety conditions. Any attempt to fire them should result in an immediate stop work from every employee in the system until they are put back on the job and the safety concerns are resolved.
[–] ktallett 14 hours ago
[–] 1718627440 15 hours ago
A written movement authority is a signal as well in railway terms. It's more like "I don't trust your second traffic light, that you placed next to the normal one, because the normal one is broken".
[–] dutchbart 17 hours ago
[–] cedws 16 hours ago
[–] delta_p_delta_x 16 hours ago
Potentially, but the point is that signallers should physically be unable to allow trains to proceed, and drivers should physically not be able to override them. British signalling from the 1800s has physical interlocks; this isn't a matter of manual versus automatic train operation. It is clearly systemic.
[–] M95D 14 hours ago
[–] kube-system 9 hours ago
The reason vehicles are still driven manually is because humans rely on transportation every day, all of the time.
[–] dns_snek 15 hours ago
If signaling worked properly then it wouldn't matter whether the train was driven autonomously or not, the "problem" becomes trivial. Establishing and continuously verifying that signaling is working properly is the hard part.
Without signaling you're limited to crawling speed just like humans are when they don't have any signalling .
[–] 1718627440 16 hours ago
The current system is basically that the train is driven both automatically and by a professional attentive driver at the same time. Changing it to just the automatic system is going to reduce safety. Also the real world is way to messy to reach acceptable availability rates with only automatic systems.
[1] https://www.itf-oecd.org/sites/default/files/spain-road-safe...
[–] fn-mote 16 hours ago
In this case the “object” was another train. That’s not the “hard” part of the problem. This sounds like an apologist comment.
[–] dns_snek 15 hours ago
Are there systems that can warn drivers and prevent collisions without external signaling, like ACAS?
[–] 1718627440 15 hours ago
[–] AnimalMuppet 10 hours ago
Detecting an object on the tracks 2 km away (say), as opposed to beside the track at the same distance, is in fact a hard problem. The tech used in self-driving cars is not going to solve it.
[–] schnitzelstoat 17 hours ago
[–] Xenoamorphous 16 hours ago
Salary for ministers is around 80k euro per year. Yes significantly more than the minimum salary but hardly a fortune.
[–] logicchains 7 hours ago
[–] baal80spam 6 hours ago
I could not believe it, but it is actually true:
The average gross annual salary in Spain is €29,540, which translates to approximately €2,461 per month before taxes.
[–] naranjito 2 hours ago
From https://relocoast.com/en/guides/minimum-wage-salary A quarter of the people do not go beyond 18K, another quarter is between that and 25K. Only one quarter make more than 36K.
Before taxes. And VAT is 21%, with some exceptions.
[–] agarsev 16 hours ago
[–] Xenoamorphous 16 hours ago
It sucks but that's how it is over here. It's "my" party the one in power when a catastrophe like this happens? It's not the politicians, it's someone else. Is it the "other" party? Surely the politicians are ultimately responsible.
This reflects on the news media as well.
[–] ChrisArchitect 7 hours ago
Spain train crash
[–] pvaldes 6 hours ago
- Not Spain. This was Bedford (UK) in June 2026.
https://en.wikipedia.org/wiki/2026_Bedford_train_collision
The train collided rear-end into the rear carriages of the other train and derailed, which also resulted in the three rear carriages of the first train to derail
- This was Białośliwie train collision (Poland) in June 2026
https://en.wikipedia.org/wiki/2026_Bia%C5%82o%C5%9Bliwie_tra...
One carriage was reported to have overturned and four more were derailed. 44 of the passengers were injured
- And this was the Cleon Derailement (France) by sabotage in September 2026
https://en.wikipedia.org/wiki/Cl%C3%A9on_derailment
In this last case Police suspected sabotage after a 300 Kg piece of rail was found deliberately laid in the railway.
"A fire was detected in the rear cabin of the high-speed train. Following safety protocols, the 283 passengers on board have been evacuated"
This was an AVE passenger train in the line Madrid-Barcelona, in October 2026. Most probably another case of sabotage.
[–] vagab0nd 9 hours ago
"Add a global memory. Whenever I'm in Spain or planning to go there, remind me of this: <story url>, and plan to avoid it."
[–] whycome 8 hours ago
[–] iSnow 5 hours ago
- trains go in tunnels or tracks are between houses. When train control systems were defined in the 1990's, there was no way to make them sensitive enough to record GPS positions. Instead there is a different location system based on so-called balises with a fixed position on the tracks. Every time a train crosses one, it knows where it is.
- Planes go in 3 dimensions, trains in one. If ATC wants to ensure two planes do not collide, they will assign them different headings and/or heights. Precise position isn't that important. Trains cannot avoid each other, that's why they move in blocks.
And yes, they do signal their position back to the control center, it's just a different protocol
It sounds like the issue happened, because there was an error in the line-based train control system (LZB), which led to falling back to the point-based train control system (ASFA). However since there are more virtual blocks in LZB, than physical blocks in ASFA, this means that suddenly more than one train is in one block, which violates the most basic assumption of train control. That requires the trains to not rely on the train control at all, even if it says that the block is clear, but instead are operated manually.
I do not know what the proper procedures for that are in Spain, but in e.g. Germany that seems to require driving by sight. However that is also only after a number of accidents due this situation. So the following seem to be similar accidents from Germany:
- https://de.wikipedia.org/wiki/Eisenbahnunfall_von_Meerbusch-...
- On April 9, 2002, a near-collision occurred near Fallersleben. After a computer at the LZB control center in Fallersleben crashed, two trains on each of the two main tracks came to a stop. When the computer was restarted, the rear train in each pair was signaled a speed of 160 km/h, while the front train in each pair was signaled 0 km/h. One of the two train operators following saw the train stopped in front of him; the other, as a precaution, contacted the operations center, which warned him not to proceed.